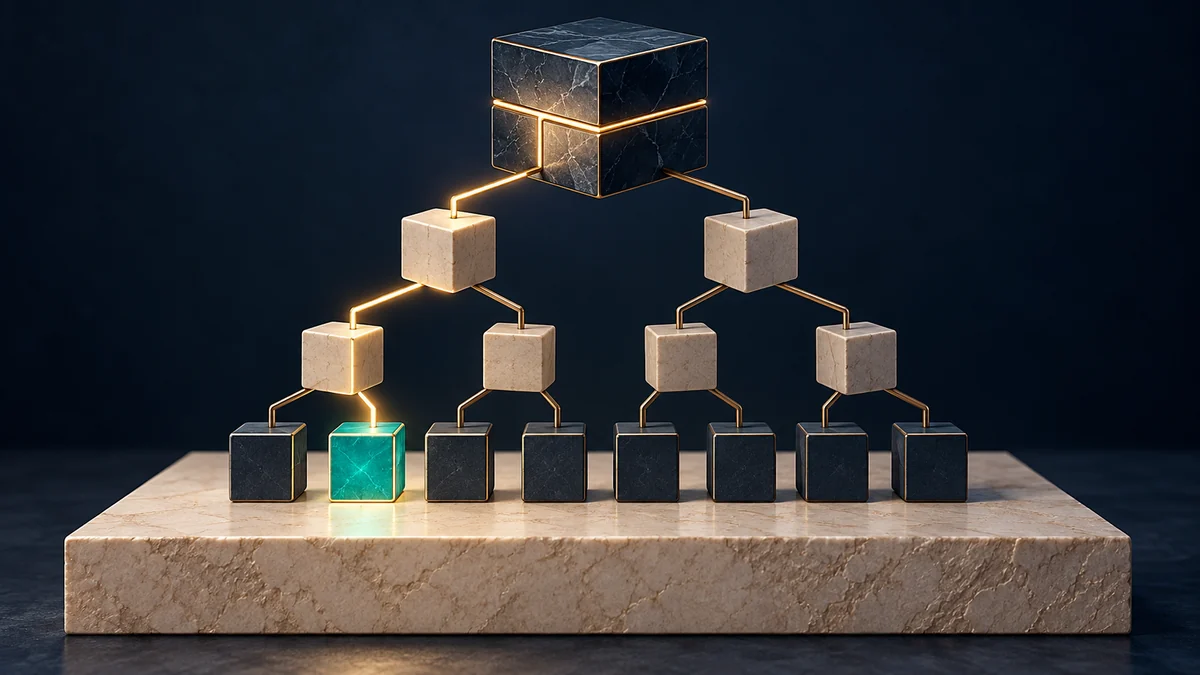
A compact proof can show how a transaction commitment connects to a particular block header without containing the entire block. Bitcoin’s white paper describes this approach in its discussion of simplified payment verification. Understanding the evidence requires identifying both the cryptographic connection and the additional assumptions used to accept the surrounding chain. Bitcoin white paper: Merkle trees and simplified payment verification, sections 7–8
Follow the evidence
Trace how the event could reach markets, then inspect a competing explanation.
Compare explanations
Switch lenses to see what each account explains—and what remains uncertain.
WFN analysis: imagine an invented block containing four transaction commitments. A branch supplies the neighboring hashes needed to recompute the root for one selected commitment. If the recomputed root matches the chosen header, the evidence connects that commitment to that header under the hashing assumptions. It does not select which header the reader should trust. This separates two questions that a receipt can compress into one green check mark. One asks whether the commitment belongs to the stated block. Another asks whether that block is part of the chain accepted by the reader’s verification method. The receipt should identify which question was actually checked and the node or service providing the surrounding evidence. A claim about payment completion adds further details: the intended transaction, receiving output, amount and chain history. A proof tied to the wrong transaction or an unrelated header would not answer the recipient’s question. The invented four-leaf tree is an explanatory model and contains no real transaction, observed payment or statement about a particular wallet’s security.
WFN analysis: imagine an invented block containing four transaction commitments. A branch supplies the neighboring hashes needed to recompute the root for one selected commitment. If the recomputed root matches the chosen header, the evidence connects that commitment to that header under the hashing assumptions. It does not select which header the reader should trust. This separates two questions that a receipt can compress into one green check mark. One asks whether the commitment belongs to the stated block. Another asks whether that block is part of the chain accepted by the reader’s verification method. The receipt should identify which question was actually checked and the node or service providing the surrounding evidence. A claim about payment completion adds further details: the intended transaction, receiving output, amount and chain history. A proof tied to the wrong transaction or an unrelated header would not answer the recipient’s question. The invented four-leaf tree is an explanatory model and contains no real transaction, observed payment or statement about a particular wallet’s security.
A useful evidence record retains the transaction identifier, block hash, height, branch data, header source and verification procedure. If using a third-party service, identify which claims come from that service rather than the reader’s own checks. This editorial record does not prescribe a specific wallet design; it makes the scope of a payment assertion easier to inspect. Later confirmations and an independently verified chain can add evidence, but their meaning depends on the system and method being used. Avoid turning the existence of a Merkle branch into a universal finality claim. The white paper supplies the original simplified-verification concept; an assessment of a modern implementation would also need its current documentation, behavior and stated threat model.
The branch and the header play different roles
The paper explains that transactions are hashed into a Merkle tree and the root is committed in the block header. Its simplified verification method obtains a branch linking a transaction to that root and follows block headers representing proof of work. The branch supplies a connection to a committed set. Bitcoin white paper: Merkle trees and simplified payment verification, sections 7–8
The paper also distinguishes this method from nodes verifying transactions for themselves and describes its vulnerability if an attacker overpowers the network. That warning concerns the verification model. A branch alone should not be described as an independent check of every consensus rule or as a guarantee that the referenced block will remain in the accepted chain. Bitcoin white paper: Merkle trees and simplified payment verification, sections 7–8
An inclusion question needs a named reference point
WFN analysis: imagine an invented block containing four transaction commitments. A branch supplies the neighboring hashes needed to recompute the root for one selected commitment. If the recomputed root matches the chosen header, the evidence connects that commitment to that header under the hashing assumptions. It does not select which header the reader should trust.
This separates two questions that a receipt can compress into one green check mark. One asks whether the commitment belongs to the stated block. Another asks whether that block is part of the chain accepted by the reader’s verification method. The receipt should identify which question was actually checked and the node or service providing the surrounding evidence.
A claim about payment completion adds further details: the intended transaction, receiving output, amount and chain history. A proof tied to the wrong transaction or an unrelated header would not answer the recipient’s question. The invented four-leaf tree is an explanatory model and contains no real transaction, observed payment or statement about a particular wallet’s security.
Describe the verification scope precisely
A useful evidence record retains the transaction identifier, block hash, height, branch data, header source and verification procedure. If using a third-party service, identify which claims come from that service rather than the reader’s own checks. This editorial record does not prescribe a specific wallet design; it makes the scope of a payment assertion easier to inspect.
Later confirmations and an independently verified chain can add evidence, but their meaning depends on the system and method being used. Avoid turning the existence of a Merkle branch into a universal finality claim. The white paper supplies the original simplified-verification concept; an assessment of a modern implementation would also need its current documentation, behavior and stated threat model.